Post

Log inSign up

Post

Log inSign up

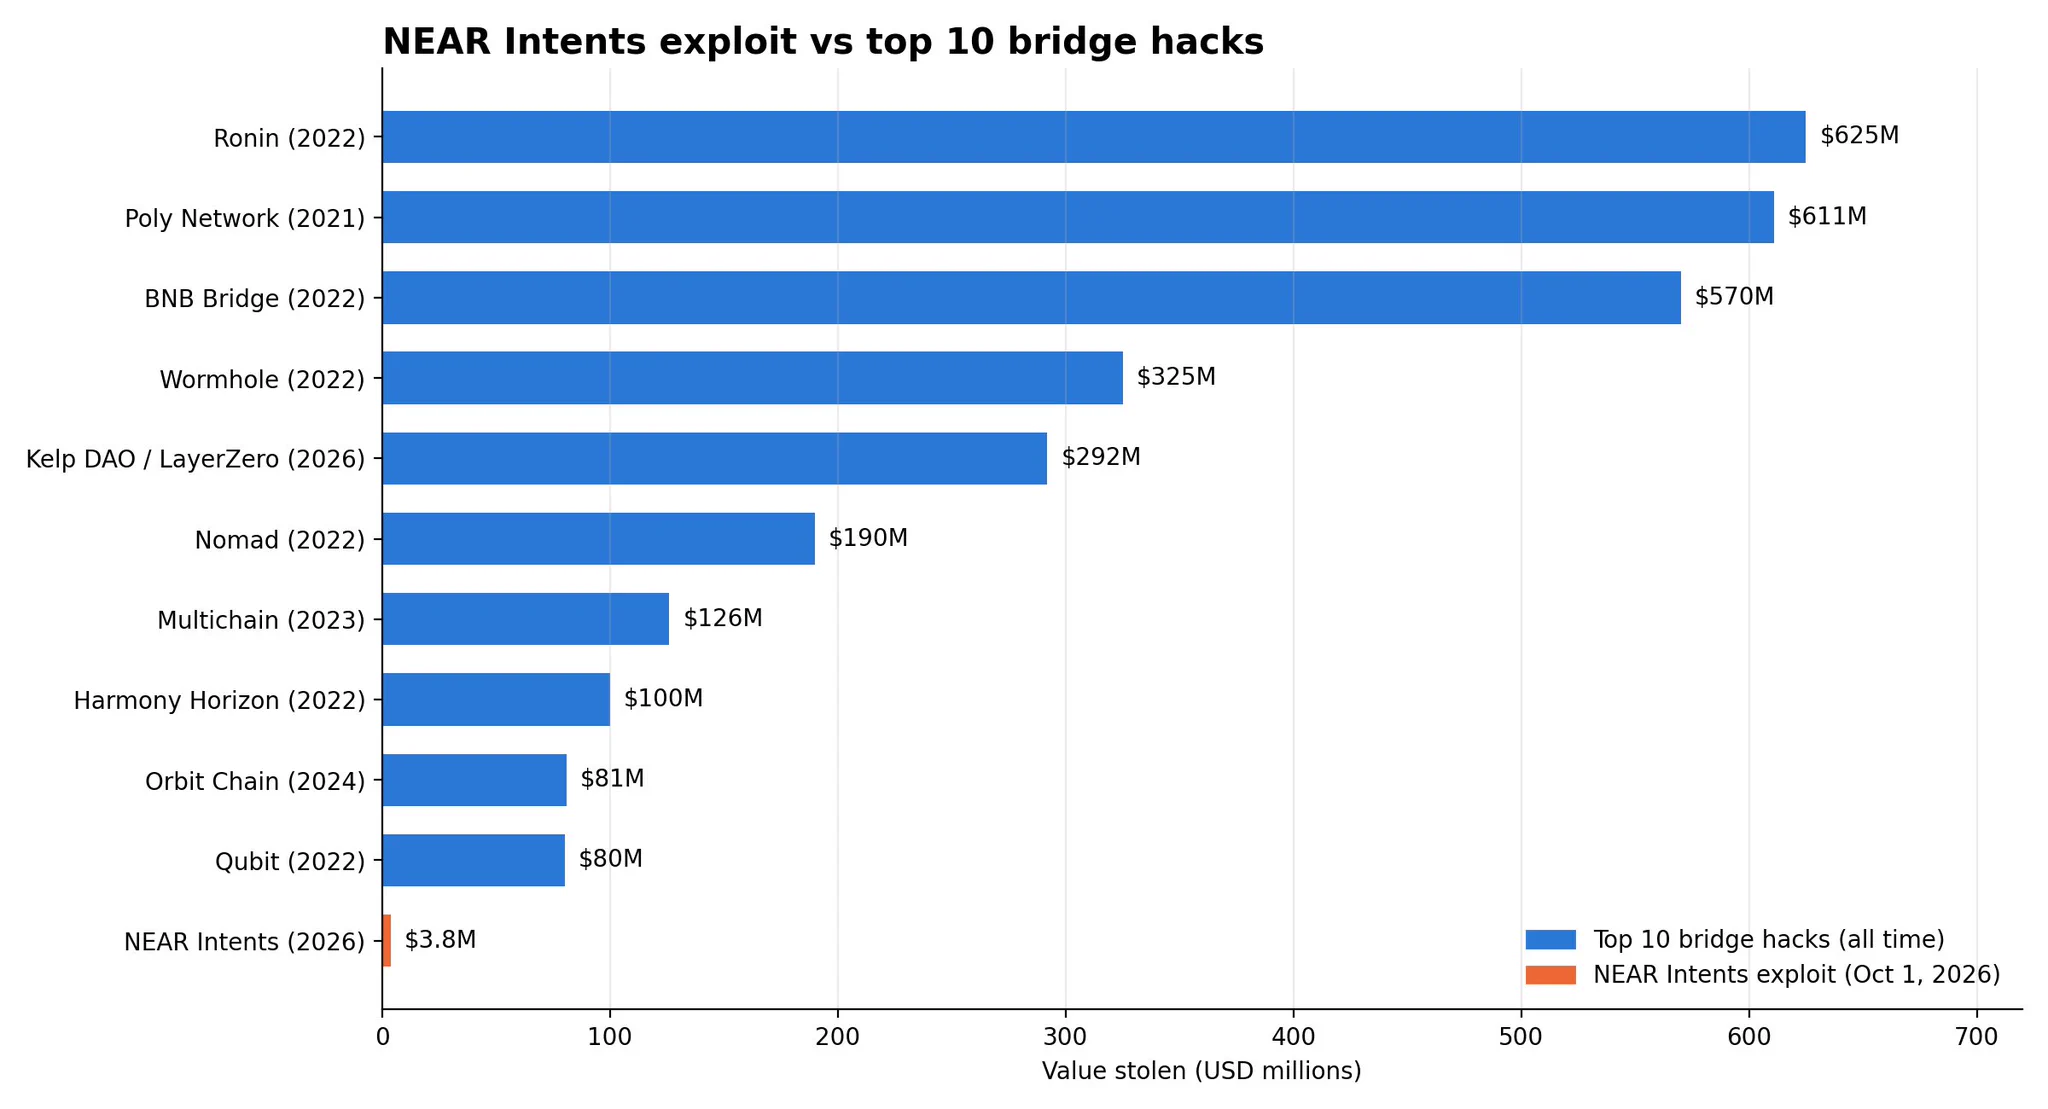
Illia (root.near) (🇺🇦, ⋈) on X: "Earlier today, NEAR Intents was exploited for $3.8m. SHIELD, the AI security layer on Intents, detected outlier behavior and Intents were temporarily paused. All of the affected users will be compensated in full. The attacker exploited a bug in the Omni deposit/withdrawal interaction with the NEAR Intents smart contract isolated to USDT on BSC. The Intents team quickly identified the exact vulnerability and it was fixed within an hour of detection. NEAR Intents and https://t.co/uilYXjPFHF are already back online, except for a few affected chains on Intents. The core NEAR Protocol, NEAR token, and other applications on NEAR were not affected. NEAR Intents now processes over $4B a month in trading and payments volume, serving as the industry’s connector across chains and ecosystems. At this scale, we have to hold ourselves to a higher security standard. This was the first major exploit on Intents and we will apply all learnings from this incident as part of a full retro and postmortem. The crypto space is entering a new era of far more sophisticated cyber attacks. Recently, we have seen BitGet, Metamask, Lido all being targeted by criminals equipped with AI systems that are continuously trying to hack all infrastructure. As a space, we need to be far more vigilant and raise the bar on both onchain contract standards and offchain monitoring and proactive prevention. This includes incorporating formal verification, a key tool for preventing a large class of vulnerabilities. The NEAR ecosystem is already working on a formal verification system for NEAR contracts and will shortly implement it as part of the release process, alongside other security measures that will come out of the postmortem. Being more proactive against criminal activity is a critical step to ensure the growth and legitimacy of crypto. It’s time to join forces and work together to use all tools at our disposal to detect and prevent malicious activity. SHIELD is our approach to monitoring and AI-based outlier detection. We welcome new SHIELD partners to work with us to share information faster and get better at detecting and containing criminals and exploits across web3."

@ilblackdragon
Illia (root.near) (🇺🇦, ⋈)
NEAR Protocol
@ilblackdragon
Earlier today, NEAR Intents was exploited for $3.8m. SHIELD, the AI security layer on Intents, detected outlier behavior and Intents were temporarily paused. All of the affected users will be compensated in full. The attacker exploited a bug in the Omni deposit/withdrawal interaction with the NEAR Intents smart contract isolated to USDT on BSC. The Intents team quickly identified the exact vulnerability and it was fixed within an hour of detection. NEAR Intents and near.com are already back online, except for a few affected chains on Intents. The core NEAR Protocol, NEAR token, and other applications on NEAR were not affected. NEAR Intents now processes over $4B a month in trading and payments volume, serving as the industry’s connector across chains and ecosystems. At this scale, we have to hold ourselves to a higher security standard. This was the first major exploit on Intents and we will apply all learnings from this incident as part of a full retro and postmortem. The crypto space is entering a new era of far more sophisticated cyber attacks. Recently, we have seen BitGet, Metamask, Lido all being targeted by criminals equipped with AI systems that are continuously trying to hack all infrastructure. As a space, we need to be far more vigilant and raise the bar on both onchain contract standards and offchain monitoring and proactive prevention. This includes incorporating formal verification, a key tool for preventing a large class of vulnerabilities. The NEAR ecosystem is already working on a formal verification system for NEAR contracts and will shortly implement it as part of the release process, alongside other security measures that will come out of the postmortem. Being more proactive against criminal activity is a critical step to ensure the growth and legitimacy of crypto. It’s time to join forces and work together to use all tools at our disposal to detect and prevent malicious activity. SHIELD is our approach to monitoring and AI-based outlier detection. We welcome new SHIELD partners to work with us to share information faster and get better at detecting and containing criminals and exploits across web3.
@near_intents
NEAR Intents
@near_intents
Oct 1
Earlier today NEAR Intents services were stopped after a security incident was detected. The incident was caused by a bug in the Omni deposit and withdrawal infrastructure interaction with NEAR Intents smart contract. The preliminary report indicates the total loss of
3:50 PM · Oct 1, 2026·
140.9K
Views
141

Log in or sign up for X

See what’s happening and join the conversation

Continue with phone
or
Log in with username or email

Relevant people

Avatar
Illia (root.near) (🇺🇦, ⋈)@ilblackdragonFollow
Co-Founder @NEARProtocol. LLM co-inventor. @ekang426 husband.

Trending now

Terms·Privacy·Cookies·Accessibility·US TIDA·Ads Info·© 2026 X Corp.
  • @ilblackdragon
    Illia (root.near) (🇺🇦, ⋈)
    NEAR Protocol
    @ilblackdragon
    Earlier today, NEAR Intents was exploited for $3.8m. SHIELD, the AI security layer on Intents, detected outlier behavior and Intents were temporarily paused. All of the affected users will be compensated in full. The attacker exploited a bug in the Omni deposit/withdrawal interaction with the NEAR Intents smart contract isolated to USDT on BSC. The Intents team quickly identified the exact vulnerability and it was fixed within an hour of detection. NEAR Intents and near.com are already back online, except for a few affected chains on Intents. The core NEAR Protocol, NEAR token, and other applications on NEAR were not affected. NEAR Intents now processes over $4B a month in trading and payments volume, serving as the industry’s connector across chains and ecosystems. At this scale, we have to hold ourselves to a higher security standard. This was the first major exploit on Intents and we will apply all learnings from this incident as part of a full retro and postmortem. The crypto space is entering a new era of far more sophisticated cyber attacks. Recently, we have seen BitGet, Metamask, Lido all being targeted by criminals equipped with AI systems that are continuously trying to hack all infrastructure. As a space, we need to be far more vigilant and raise the bar on both onchain contract standards and offchain monitoring and proactive prevention. This includes incorporating formal verification, a key tool for preventing a large class of vulnerabilities. The NEAR ecosystem is already working on a formal verification system for NEAR contracts and will shortly implement it as part of the release process, alongside other security measures that will come out of the postmortem. Being more proactive against criminal activity is a critical step to ensure the growth and legitimacy of crypto. It’s time to join forces and work together to use all tools at our disposal to detect and prevent malicious activity. SHIELD is our approach to monitoring and AI-based outlier detection. We welcome new SHIELD partners to work with us to share information faster and get better at detecting and containing criminals and exploits across web3.
    @near_intents
    NEAR Intents
    @near_intents
    Oct 1
    Earlier today NEAR Intents services were stopped after a security incident was detected. The incident was caused by a bug in the Omni deposit and withdrawal infrastructure interaction with NEAR Intents smart contract. The preliminary report indicates the total loss of
    3:50 PM · Oct 1, 2026·
    140.9K
    Views
    141
  • @defijangle
    Jangle
    @defijangle
    Oct 1
    Incredible response time 🛡️
  • @DesChan13
    deez | survival arc
    @DesChan13
    Oct 1
    For reference
  • @Dashpay
    Dash
    @Dashpay
    Oct 1
    Sorry to see this happened, but we're happy to see your professionalism in handling this. We'll get through this era of exploits soon.