3 Easy Steps
One Unified Platform

Analyze & Profile CVEs


Replace with Near-Zero CVE Images

Optimize & Harden

What Makes RapidFort the Smarter Choice

Faster Releases
Built on trusted LTS Linux distributions including Ubuntu, RHEL, Debian, and Alpine with no proprietary OS lock-in.

End-to-End Container Security
Analyze vulnerabilities, understand runtime behavior, harden containers, and validate compliance in one platform.

Full Stack Risk Reduction
Secure both third-party dependencies and first-party application components across your container software stack.

Built for Enterprise and Federal Security
Integrated support for STIG and CIS security benchmarks used in regulated and mission-critical environments.

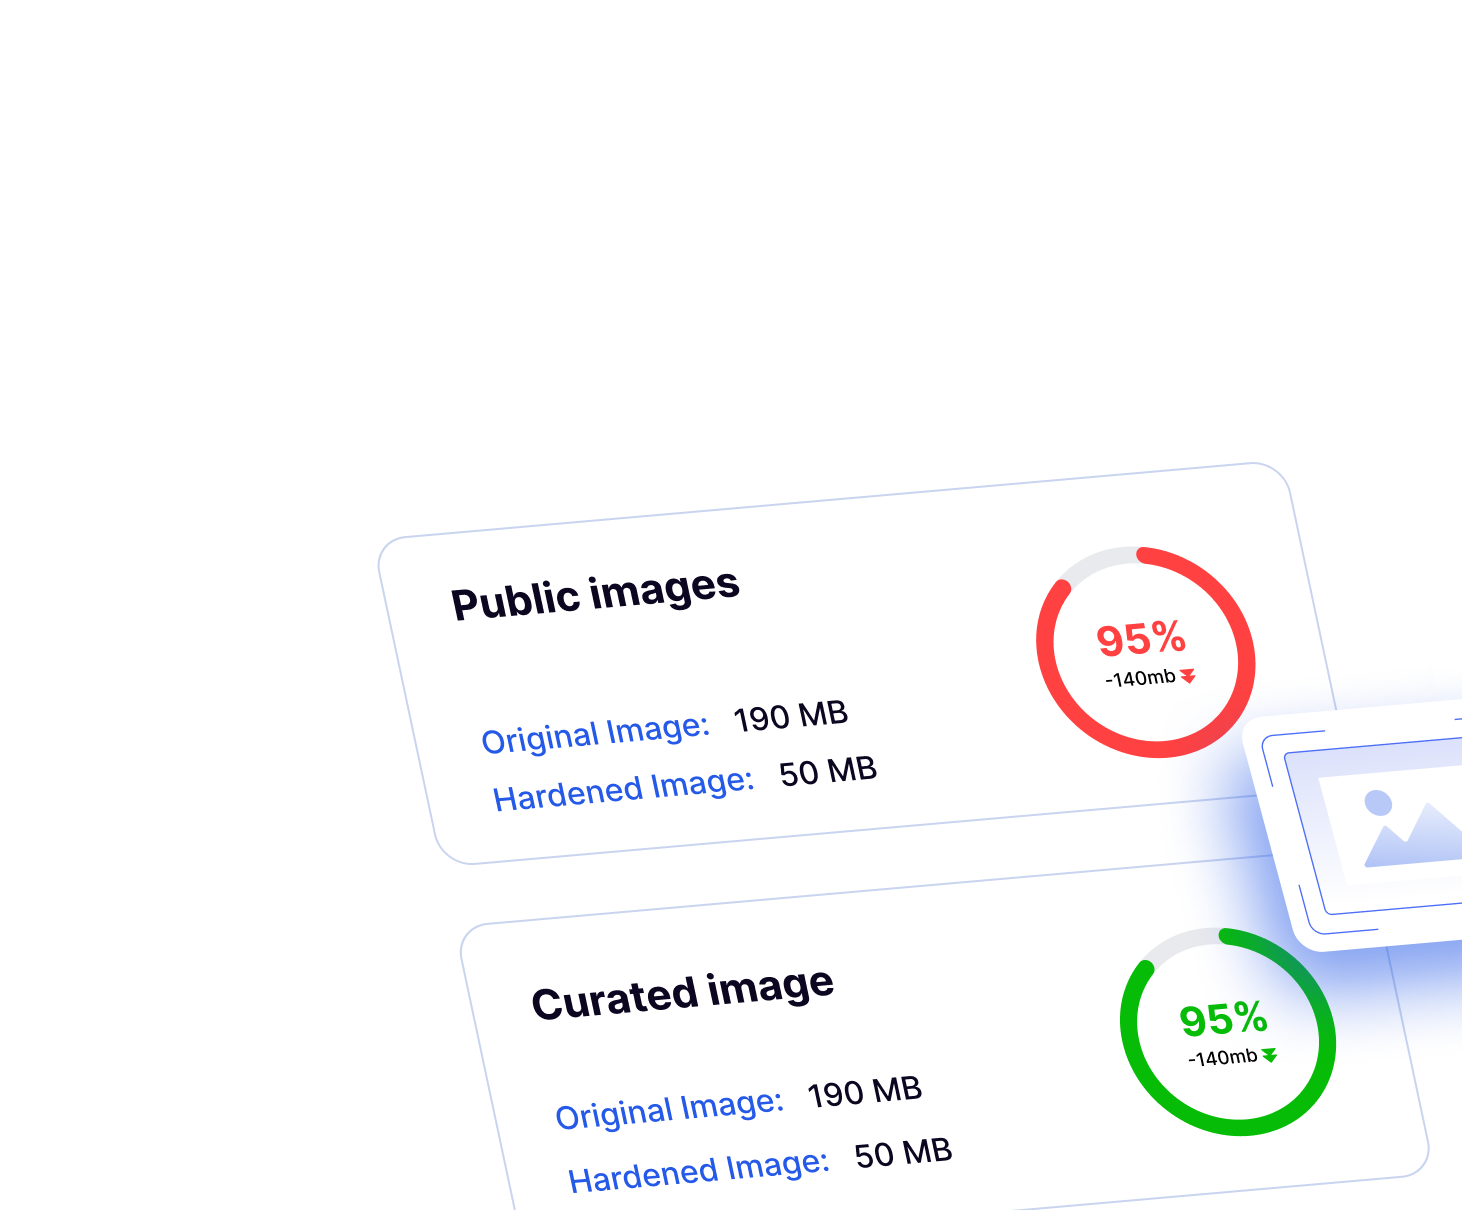
Patched Vs Daily Build
RapidFort Curated Images are patched with minimal code changes to maintain stable, production-ready container images.
Built to Eliminate Risk, Accelerate Compliance, and Reduce Costs

90%
Attack Surface Reduction
Remove dormant, unused, and unreachable components

100%
Real Execution Path Visibility
See exactly what runs - and what never should

82M
Packages Secured
Scanned, profiled, and monitored via DevTime and RunTime tools.

124 M
Vulnerabilities Removed
Eliminated through container hardening - no code changes required.

Up to 99.9%
CVE Elimination
Eliminate vulnerabilities continuously without code changes

1M+
Images Hardened
Optimized Containers by reducing software attack surface
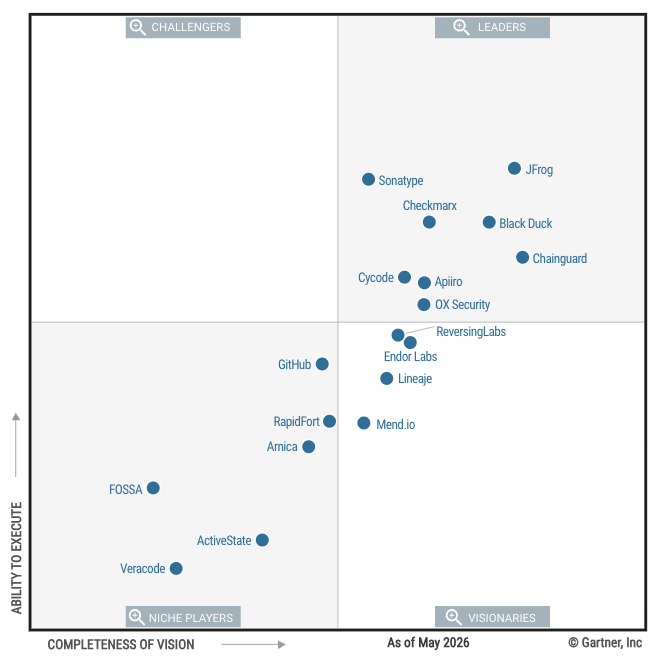
Trusted by Your Peers.
Securing the Global Software Supply Chain


RapidFort Software Supply Chain Security Platform
The only platform that starts secure and stays secure - from base image to production runtime.

RapidFort Analyzer

RapidFort Profiler

RapidFort Curated Images

RapidFort Curated Libraries

RapidFort Optimizer

RapidFort CART

Accurate Container Vulnerability Analysis with Less Noise
Scan container images across CI/CD pipelines, registries, and Kubernetes environments while reducing up to 25% vulnerability noise so teams can focus on real, actionable risk.
Runtime Visibility into What Actually Runs in Production
Identify which software components are actively executed inside containers so teams can prioritize vulnerabilities tied to real runtime exposure instead of theoretical risk.

35,000+ Curated Near-Zero CVE Container Images
Start from production-ready container images that are continuously patched and hardened to eliminate inherited vulnerabilities before applications are deployed.

Malware-Scanned Curated Libraries
Consume trusted open-source libraries that are continuously malware-scanned and curated before they enter your build pipelines, artifacts, or production environments.

Automatically Reduce Container Attack Surface
Remove unused components and rebuild usage-based hardened container images every 24 hours to minimize exploitable surface area without breaking application functionality.

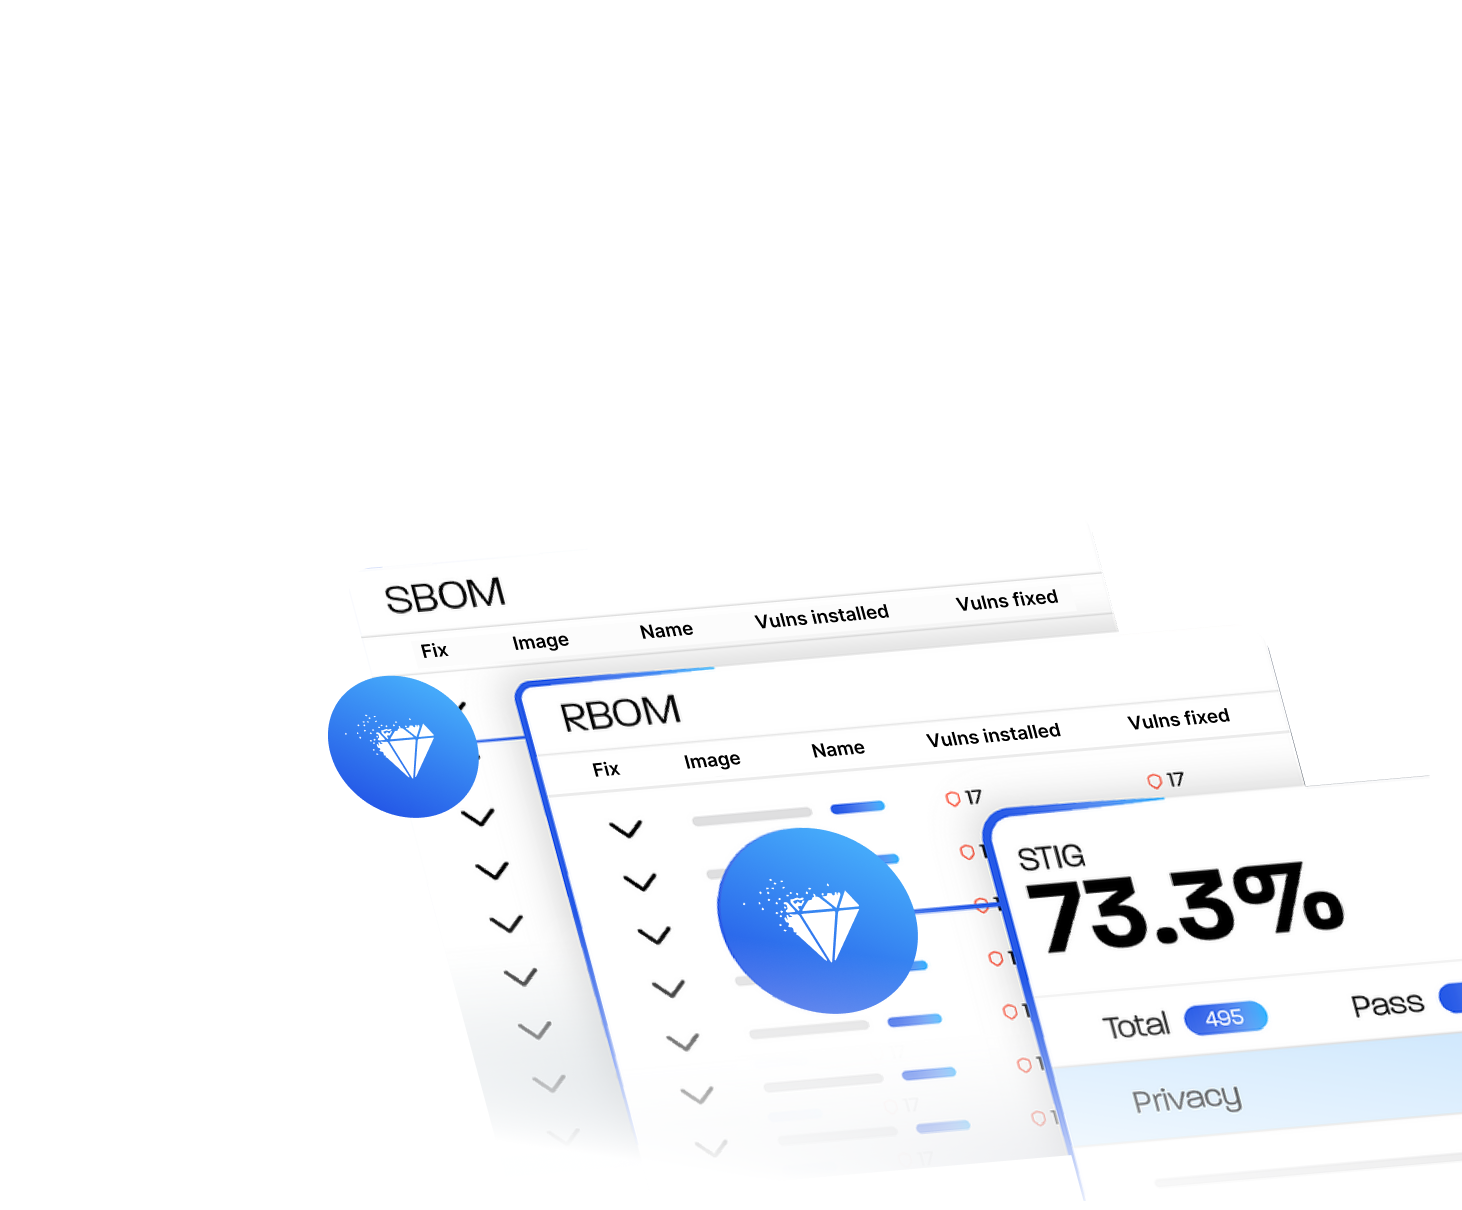
Continuous Compliance Validation for Container Environments
Automatically evaluate container images against security benchmarks and generate remediation guidance and audit-ready compliance reports across your delivery pipeline.
How Teams Use RapidFort
Solve real container security challenges across development and production.


Continuous Vulnerability Elimination
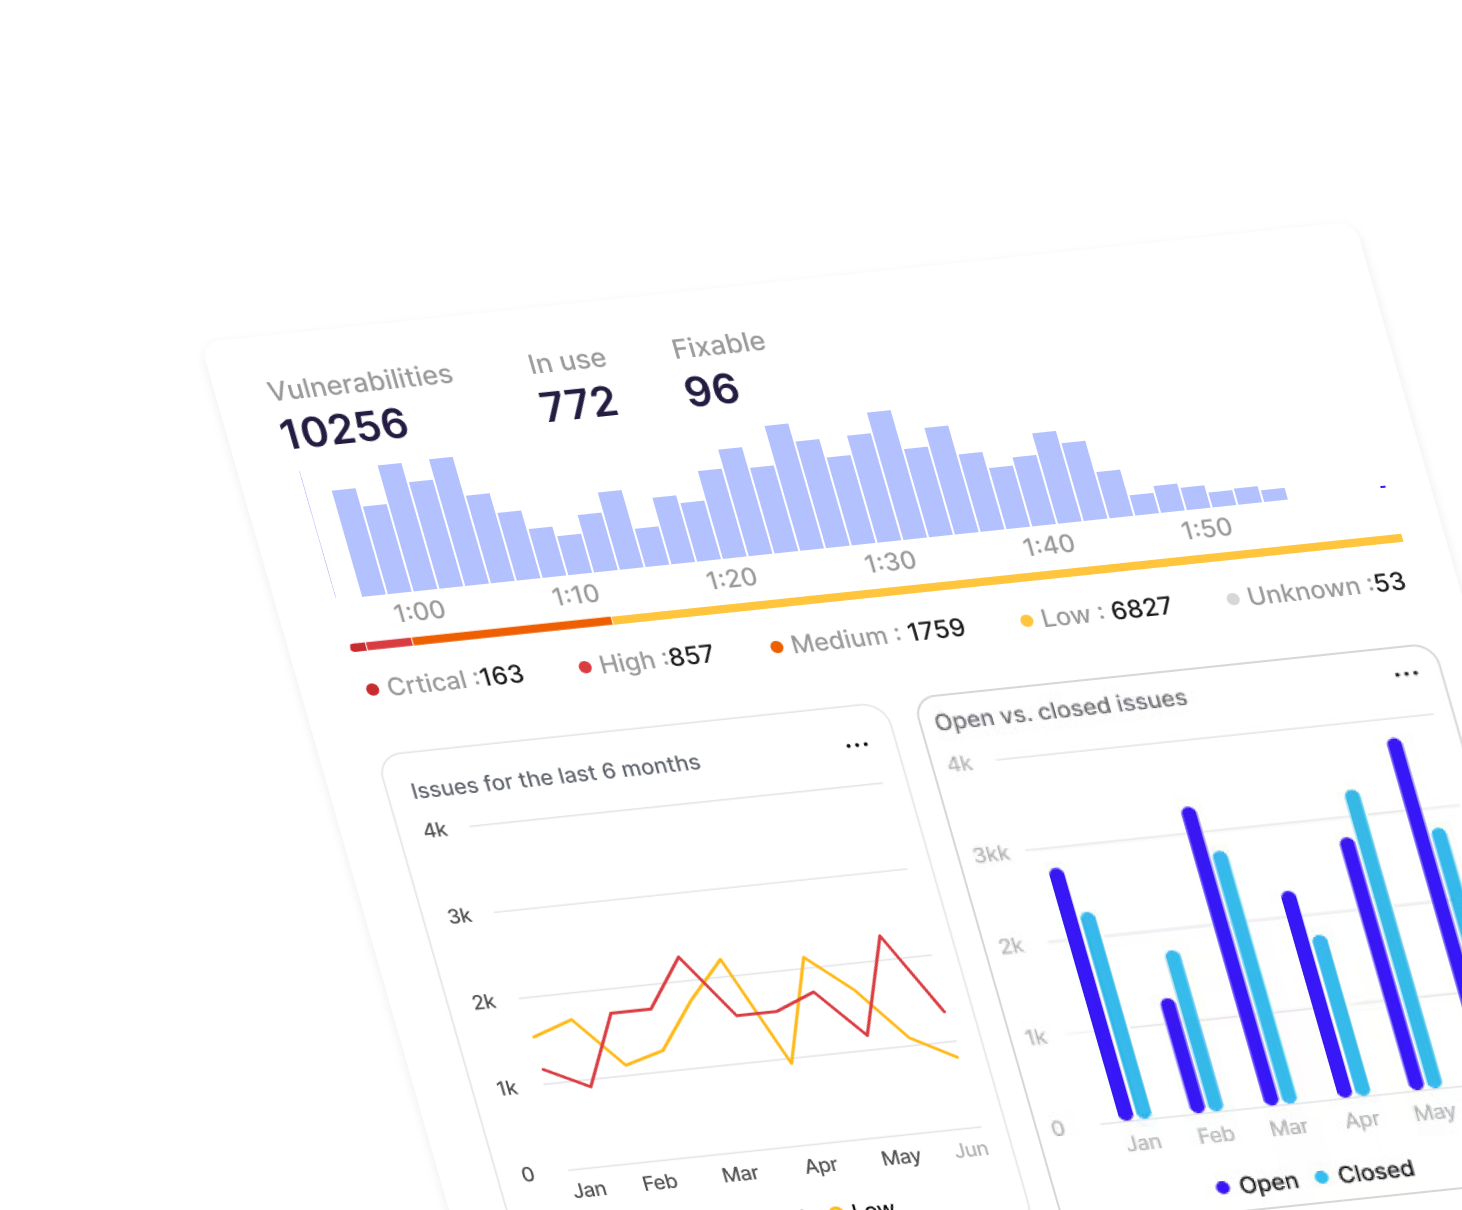
Security teams often spend days triaging vulnerabilities across container images, dependencies, and development pipelines.
RapidFort analyzes container software, prioritizes real security risks, and automates remediation workflows. Teams can eliminate up to 99.9% of CVEs without application code changes, reducing remediation effort and accelerating secure releases.

Secure Container Images
Modern applications inherit thousands of vulnerabilities from base images and open source dependencies used in container environments.
RapidFort provides 35,000+ curated near-zero CVE container images built on trusted Linux distributions. These production-grade images provide secure application foundations while avoiding proprietary operating system lock-in.
Software Attack Surface Management
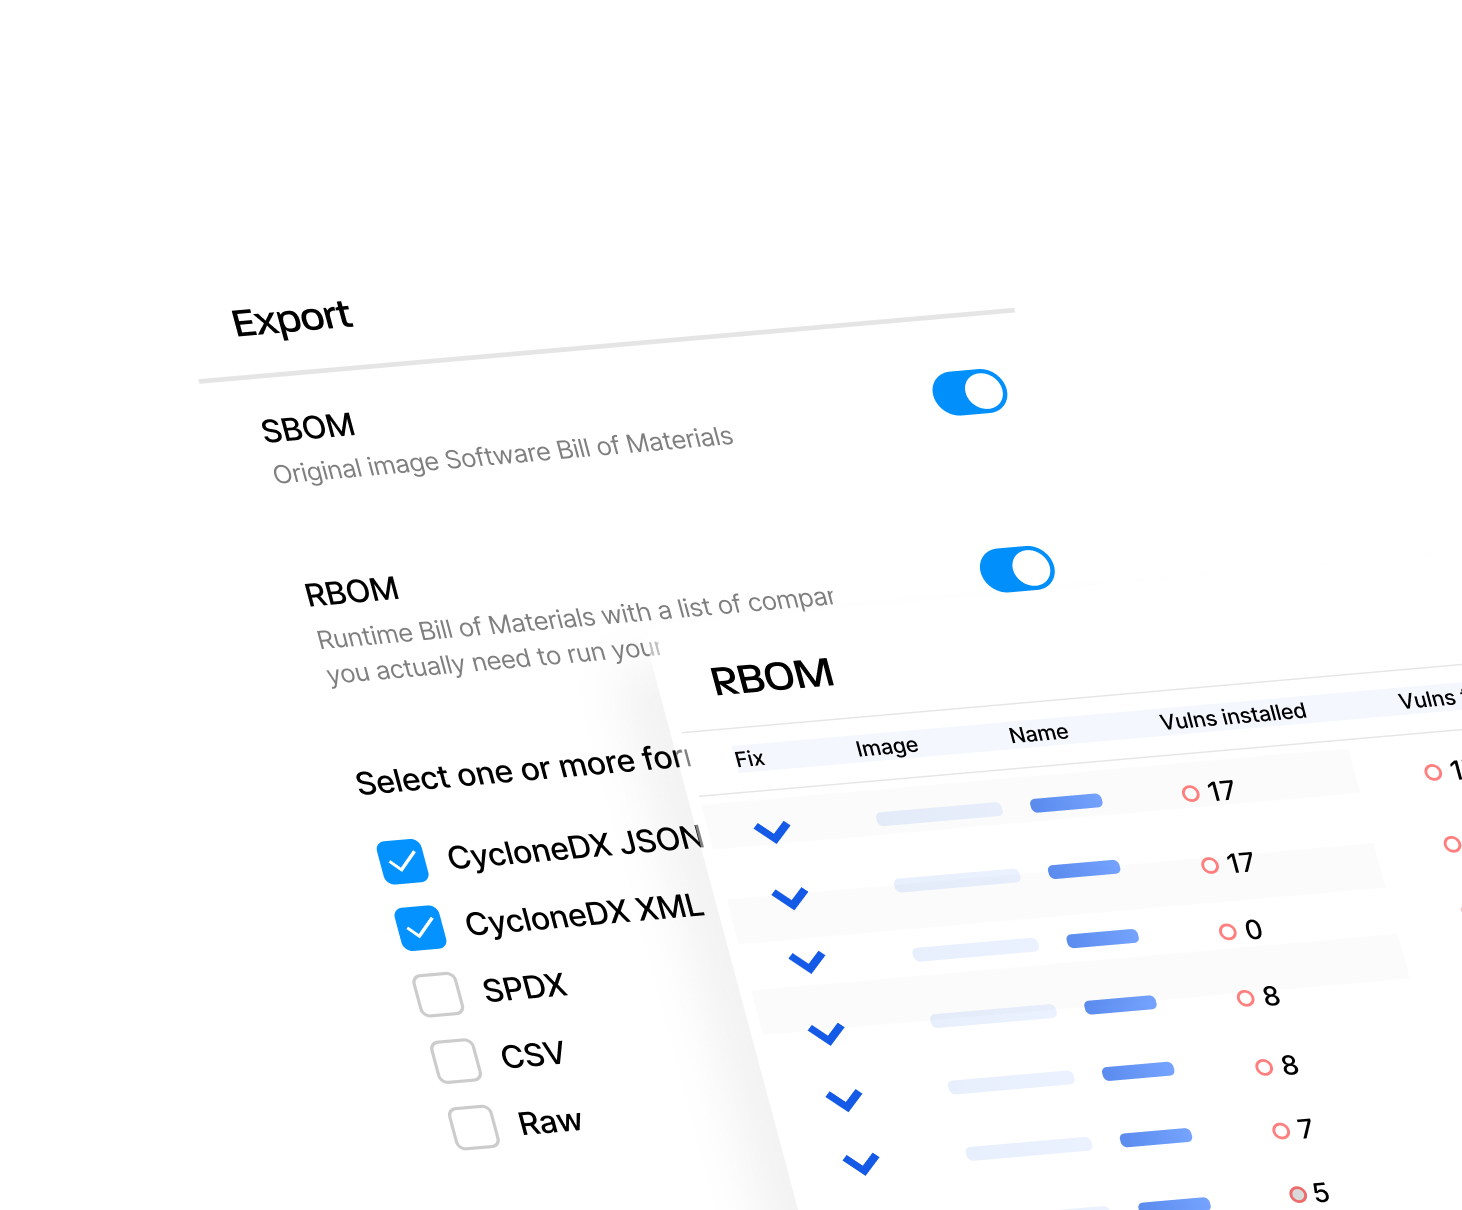
Container images contain large amounts of unused software that expand the attack surface but remain invisible to traditional scanning tools.
RapidFort analyzes real runtime behavior to identify unused components and automatically removes unnecessary packages and dependencies, reducing the attack surface by 60–90% while preserving full application functionality.
Accelerate Compliance Readiness
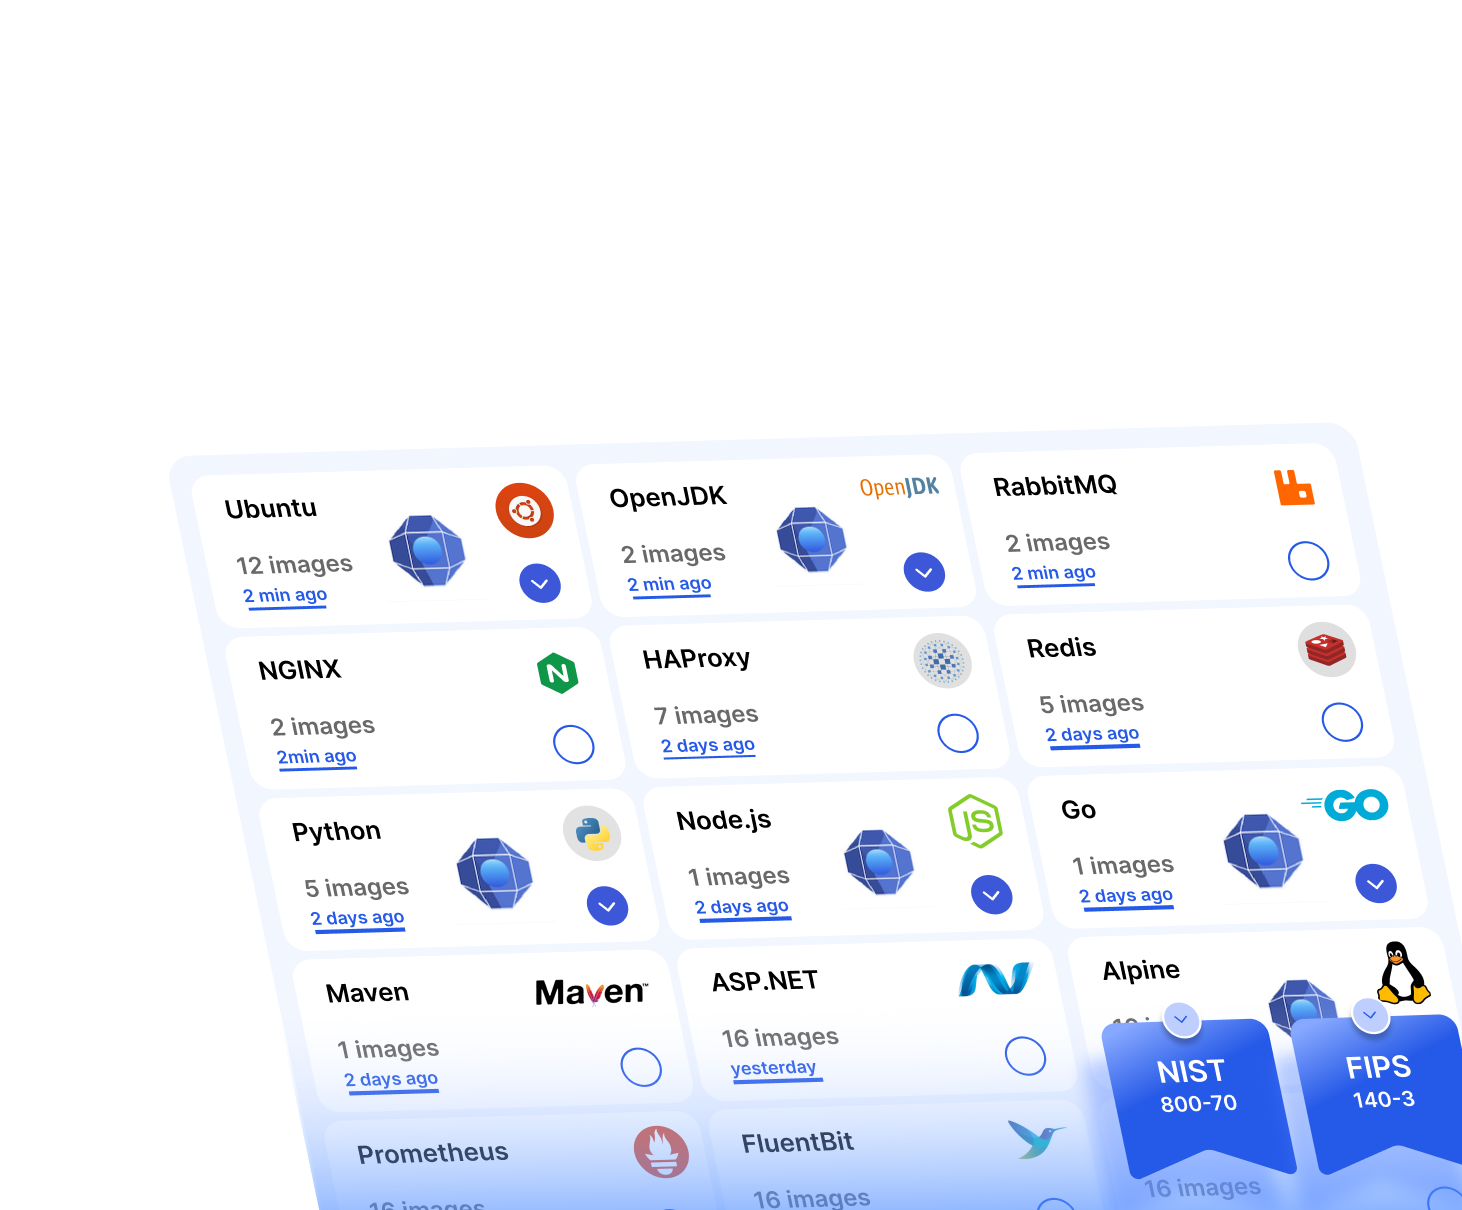
Meeting standards such as FedRAMP, CMMC, CRA, SOC 2, and CIS benchmarks requires continuous vulnerability management and hardened software environments.
RapidFort reduces inherited vulnerabilities, validates security baselines, and generates continuous compliance evidence to help organizations accelerate certification and maintain audit-ready systems.
Runtime Protection
Security risks evolve once containerized applications are running in production environments.
RapidFort provides runtime visibility into container behavior and software usage, allowing teams to identify which components are actually executed and prioritize vulnerabilities tied to the active attack surface.
Secure by Design. Trusted by Federal and Enterprise Partners.
From containerized SaaS to classified infrastructure, RapidFort supports trusted vendors securing the software supply chain at scale.






Integrate RapidFort Directly Into Your Existing Workflows and Tech Stack
Frequently Asked Questions
Answers to Your Most Common Questions