Repository navigation
Tokenizer crash when redirecting input to stdin #94360

Description

Hi!
We were doing some fuzzing using AFL for latest version 3.10.5, and we found an interesting issue.
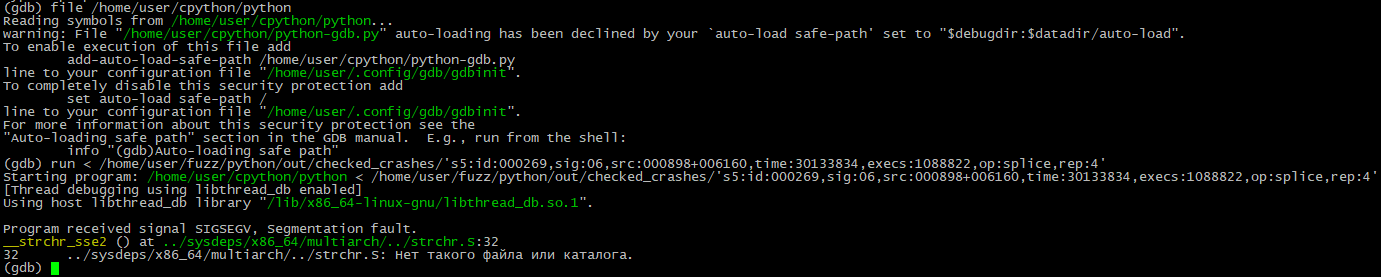
There is some crash that may be exploitable. I check latest version from git and crash was reproduced.
So input file attached with screenshots


Activity
mimicria commentedon Jun 28, 2022
This is file name for input, file is included in archive input.tar.gz (attached) also with GDB commands to use, such as
kumaraditya303 commentedon Jun 28, 2022
Can you copy and paste the GDB backtrace rather than a screenshot?
mimicria commentedon Jun 28, 2022
arhadthedev commentedon Jun 28, 2022
@mimicria My bad, I've already found that it's enough to install https://github.com/jfoote/exploitable and feed the attached
gdb_scriptinto gdb.That's why I deleted my comment hoping that nobody've seen it.
arhadthedev commentedon Jun 28, 2022
I currently have no access to a Linix machine so I can't create a debug build to get a nice stack trace from gdb.
zware commentedon Jun 28, 2022
I've reduced the reproducer to
b'#coding:latin1\n#\x00\n#\x00\n\xff a\n'and confirmed the crash in3.10,3.11, andmainafter 261a452 (GH-25050; cc @pablogsal, @erlend-aasland, @serhiy-storchaka).Interestingly, the very similar
b'#coding:latin1\n#\x00\n\x00\n\xff a\n'crashes 3.10, but appears to have been fixed in 3.11 and later by @pablogsal in GH-29654, which backports cleanly to 3.10 but does nothing for the form with third line commented.Also note that this only appears to reproduce with
./python < reproducer; about every other form I've tried (subprocess.run(sys.executable, input=b'reproducer'),cat reproducer | ./python,./python <(cat reproducer),./python reproducer, etc.) results in a properSyntaxError.For a self-contained reproducer that still requires Bash:
Hopefully this is helpful, but this is about all I can contribute here.
[-]Crash found[/-][+]Tokenizer crash when redirecting input to stdin [/+]gh-94360: Fix a tokenizer crash when reading encoded files with synta…
pythongh-94360: Fix a tokenizer crash when reading encoded files with…
gh-94360: Fix a tokenizer crash when reading encoded files with synta…
[3.10] pythongh-94360: Fix a tokenizer crash when reading encoded fil…
[3.10] gh-94360: Fix a tokenizer crash when reading encoded files wit…
vincedani commentedon Feb 20, 2023
Hello @mimicria, it looks like you are (or were) fuzzing this repository, and you’ve found some interesting bugs. 🥇
I would like to create a Python based test case reduction test suite that contains fuzzer generated outputs, and benchmark automatic test case reducers how they perform on Python inputs. It looks like to me you have opened this issue with the already reduced input that caused malfunction. Is it possible that you still have the output of the fuzzer, which is free of any reduction?
Thanks in advance,
Daniel
mimicria commentedon Feb 20, 2023
Hello, Daniel!
Python inputs that cause crashes are not reduced after fuzzing, just packaged in an archive (issue starting message).
vincedani commentedon Feb 20, 2023
Thank you @mimicria, I'll try to use that artifact.