[CVE-2020-8315] Unsafe dll loading in getpathp.c on Win7 #83582

Description

Note: these values reflect the state of the issue at the time it was migrated and might not reflect the current state.
Show more details
GitHub fields:
assignee = 'https://github.com/zooba'
closed_at = <Date 2020-01-31.02:14:13.825>
created_at = <Date 2020-01-21.01:02:15.447>
labels = ['type-security', '3.7', '3.8', 'OS-windows']
title = '[CVE-2020-8315] Unsafe dll loading in getpathp.c on Win7'
updated_at = <Date 2020-01-31.02:14:13.824>
user = 'https://github.com/anthonywee'
bugs.python.org fields:
activity = <Date 2020-01-31.02:14:13.824>
actor = 'ned.deily'
assignee = 'steve.dower'
closed = True
closed_date = <Date 2020-01-31.02:14:13.825>
closer = 'ned.deily'
components = ['Windows']
creation = <Date 2020-01-21.01:02:15.447>
creator = 'anthonywee'
dependencies = []
files = ['48855']
hgrepos = []
issue_num = 39401
keywords = ['patch']
message_count = 17.0
messages = ['360348', '360350', '360529', '360858', '360882', '360933', '360935', '360946', '360994', '360997', '360998', '360999', '361013', '361014', '361022', '361038', '361088']
nosy_count = 10.0
nosy_names = ['paul.moore', 'vstinner', 'tim.golden', 'jkloth', 'ned.deily', 'zach.ware', 'eryksun', 'steve.dower', 'miss-islington', 'anthonywee']
pr_nums = ['18231', '18232', '18233', '18234']
priority = None
resolution = 'fixed'
stage = 'resolved'
status = 'closed'
superseder = None
type = 'security'
url = 'https://bugs.python.org/issue39401'
versions = ['Python 3.6', 'Python 3.7', 'Python 3.8']
Activity
anthonywee commentedon Jan 21, 2020
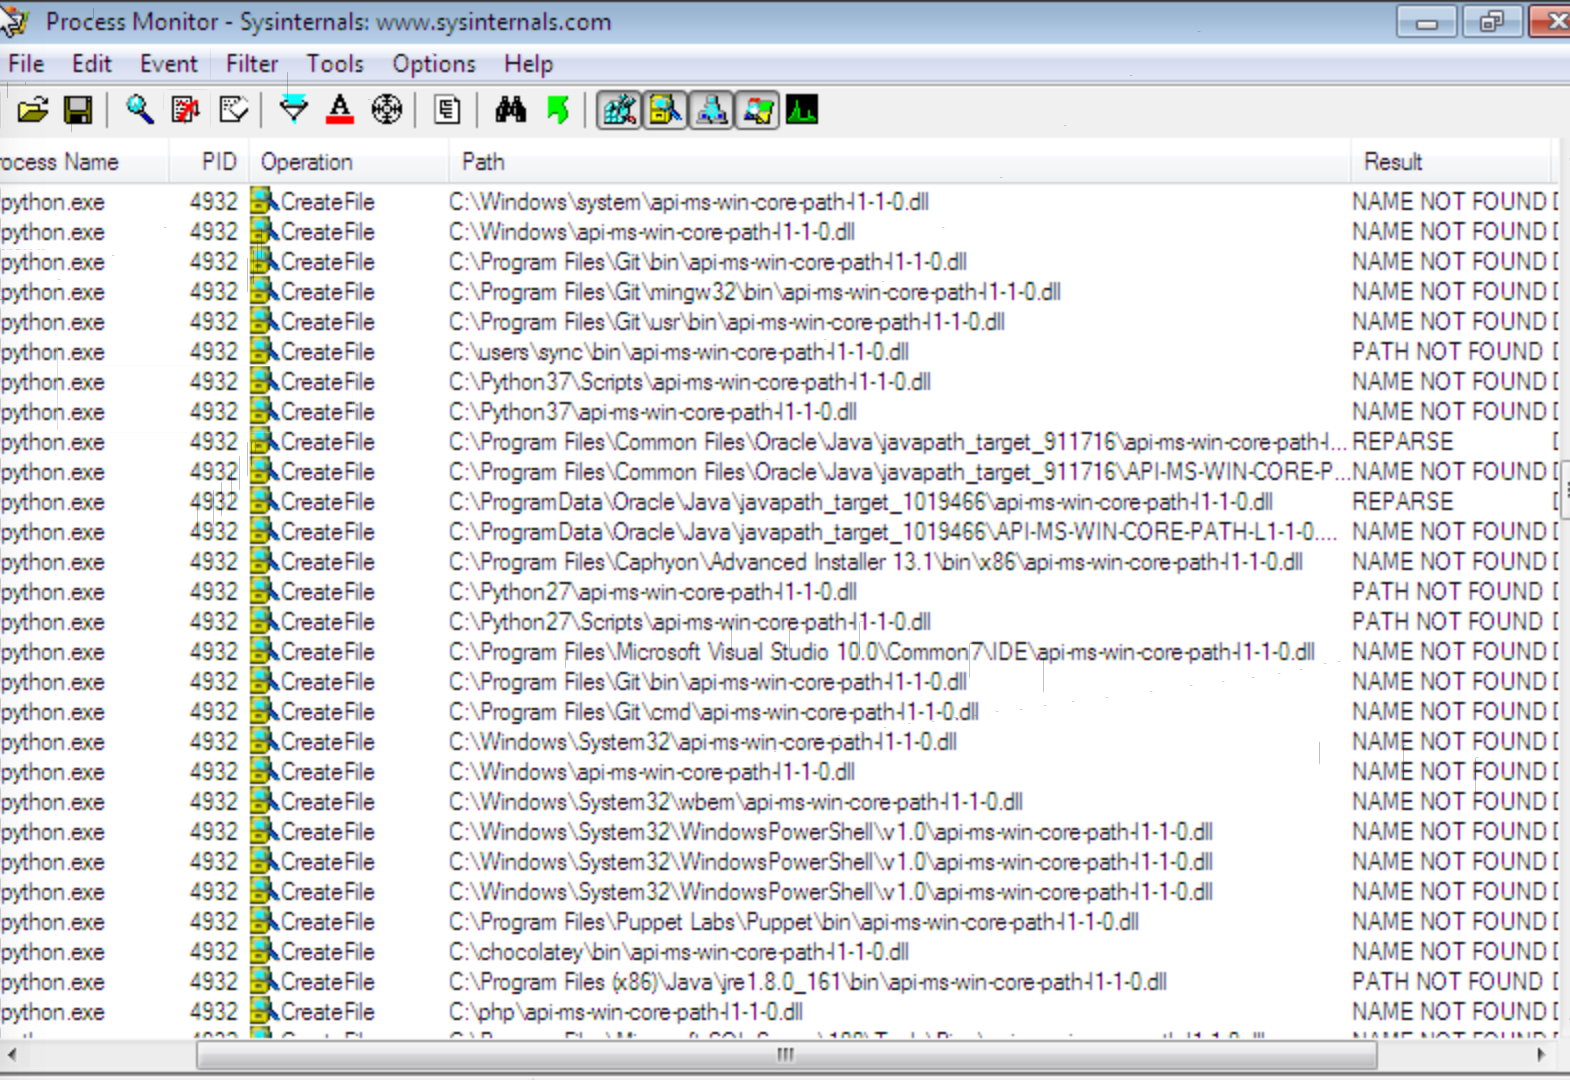
On Win7, running Python in the terminal will attempt to load the "api-ms-win-core-path-l1-1-0.dll" from various paths outside of the Python directory and the C:\Windows\System32 directories. This behavior can be verified using Process Monitor (see attachment).
This is happening due to direct calls to LoadLibraryW() in getpathp.c without any "LOAD_LIBRARY_SEARCH*" flags.
In join():
cpython/PC/getpathp.c
Line 255 in c02b41b
and canonicalize():
cpython/PC/getpathp.c
Line 291 in c02b41b
For both cases, the methods they are trying to load from api-ms-win-core-path-l1-1-0.dll (PathCchCanonicalizeEx and PathCchCombineEx) were introduced in Win8.
I tested on Win7 and Win10 and they differ in how they load these api-ms-win-* dll's and whether they appear in process monitor. In Win7, a CreateFile event appears in procmon, while in Win10 it seems like the OS is automatically loading the module from kernelbase.dll. Also in Win7 the loading of api-ms-win-core-path-l1-1-0.dll will fail while in Win10 it succeeds. However, in Win7 when it fails it results in the standard dll search strategy, which will eventually search outside of the secure directories such as the directories in the PATH env var: https://docs.microsoft.com/en-us/windows/win32/dlls/dynamic-link-library-search-order
Each of the problematic methods in cpython have a pattern of attempting to load the dll, then falling back to an older version of the method. Thus in Win7, the dll fails to load and it falls back to the older version of the method. In Win10, the dll load succeeds and we use the new versions of the methods.
I'm working on a fix to pass the LOAD_LIBRARY_SEARCH_DEFAULT_DIRS flag to limit to the dll search path scope.
eryksun commentedon Jan 21, 2020
"api-ms-win-core-path-l1-1-0.dll" is not assigned in the API set schema (in ApiSetSchema.dll) in Windows 7. Since the name is neither in the list of known DLLs nor the list of assigned API sets, the loader searches for it in the normal way. (FYI, the number of API sets increased from 35 in Windows 7 up to 502 in Windows 8.1.)
I think this could use just LOAD_LIBRARY_SEARCH_SYSTEM32. I see no reason to try to load "api-ms-win-core-path-l1-1-0.dll" from the application directory or user directories.
I'm adding 3.6-3.9 to the list of affected versions. In 3.9 it can use a static import instead (i.e. remove LoadLibraryaExW / GetProcAddress), since only Windows 8.1+ is supported.
zooba commentedon Jan 23, 2020
Agreed, we can just search System32 for this. Thanks for doing the patch!
For future reference, and for anyone else reading this, we generally prefer unavoidable DLL hijacking bugs to come to the Python Security Response Team first (security@python.org).
zooba commentedon Jan 28, 2020
For clarity, I'm removing 3.9 from the affected versions. This version does not support Windows 7, and only Windows 7 is vulnerable to this DLL hijack.
Also submitting the CVE request.
eryksun commentedon Jan 28, 2020
I added 3.9 for the related issue to switch to using a static import, since Windows 7 isn't supported in 3.9. But I guess that should have been made a separate issue, or added to the omnibus issue bpo-32592.
zooba commentedon Jan 29, 2020
This is now assigned CVE-2020-8315 (https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-8315 https://nvd.nist.gov/vuln/detail/CVE-2020-8315)
Thanks Anthony for the report! I included your name as the reporter, though I don't see it on any of the pages.
[-]Unsafe dll loading in getpathp.c on Win7[/-][+][CVE-2020-8315] Unsafe dll loading in getpathp.c on Win7[/+]2 remaining items
vstinner commentedon Jan 29, 2020
I added https://python-security.readthedocs.io/vuln/unsafe-dll-load-windows-7.html to track fixes in all branches.
jkloth commentedon Jan 29, 2020
As noted on the PR landing page, this PR has caused failures of 2 buildbots:
https://buildbot.python.org/all/#builders/81/builds/272
https://buildbot.python.org/all/#builders/150/builds/227
(both are Windows 7)
zooba commentedon Jan 30, 2020
Both of those buildbots should be retired (or repurposed for versions of Python that still support Windows 7) :)
eryksun commentedon Jan 30, 2020
The master branch should no longer get built on Windows 7 machines. The initial build succeeds, but running "_freeze_importlib[_d].exe" fails with STATUS_DLL_NOT_FOUND (0xC0000135, i.e. -1073741515) since "api-ms-win-core-path-l1-1-0.dll" (linked from pathcch.lib) is not a Windows 7 API set.
zooba commentedon Jan 30, 2020
Thanks, Victor!
Python 2.7 and 3.5 are not vulnerable. The issue was added in 3.6 when I added support for installing Python into a long path name on up-to-date OS, which required dynamically loading an OS function. That dynamic load was the problem.
miss-islington commentedon Jan 30, 2020
New changeset 561c597 by Steve Dower in branch '3.7':
[3.7] bpo-39401: Avoid unsafe DLL load on Windows 7 and earlier (GH-18231) (GH-18232)
561c597
miss-islington commentedon Jan 30, 2020
New changeset ad4a20b by Steve Dower in branch '3.8':
[3.8] bpo-39401: Avoid unsafe DLL load on Windows 7 and earlier (GH-18231) (GH-18234)
ad4a20b
vstinner commentedon Jan 30, 2020
Oh ok, I updated the page to reflect that. I also added 3.7 & 3.8 commits.
anthonywee commentedon Jan 30, 2020
No problem! Thanks Steve, Eryk, and Victor for jumping on this!
ned-deily commentedon Jan 31, 2020
New changeset 51332c4 by Steve Dower in branch '3.6':
[3.6] bpo-39401: Avoid unsafe DLL load on Windows 7 and earlier (GH-18231) (GH-18233)
51332c4