

This permission system is available in Onyx v4.7 and later. If you are using an older version,
see Users and Groups before v4.7.
The Permission Layers
Think of permissions as layers. Each layer can add more access for a user.The layers show how far access reaches, not a strict ranking.
A Group Manager and a group permission are different mechanisms:
a Group Manager’s access always stays inside the groups they manage,
while a group permission applies across the whole organization. Depending on what you grant,
one is not automatically “more” than the other.
Default Groups
Onyx includes two default groups:
Standard users are assigned to default groups based on their access level.
Custom groups let you grant specific permissions to the users in that group.
Custom groups and configurable group permissions require a Business or Enterprise plan, or Onyx Cloud.
Community Edition has the Admin and Basic groups only.
Service Accounts and Groups
A service account gets its access the same way a user does: from the groups it belongs to. You choose those groups in the Groups selector when you create the API key. A service account that belongs to no group can post to chat, but it cannot search and it cannot reach any admin page. Only service accounts land here; regular users always start in a group.How Onyx Calculates a User’s Permissions
Onyx checks every group a user belongs to and combines the permissions from those groups. If the same user is also made a Group Manager from a group detail page, Onyx adds that scoped manager access too. For example, say Priya has these assignments:
Priya receives all three sets of access. The Analytics Viewers group does not limit her Engineering manager access,
and her Engineering manager access does not remove anything from Basic.
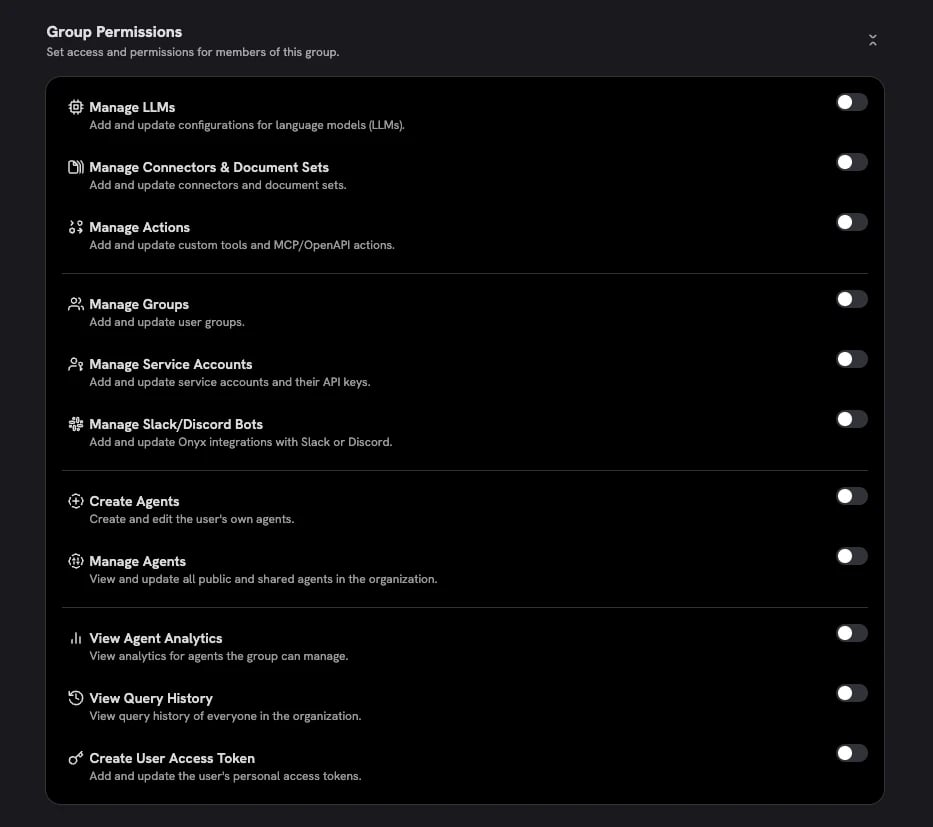
Group Permissions
Group permissions are granted to a group and apply to every member of that group. Common examples:- Give an IT administrators group Manage Connectors & Document Sets so they can manage all connectors.
- Give a model operations group Manage LLMs so they can configure language models.
- Give an analytics group View Query History so they can review query activity.
- Give a developer platform group Manage Actions so they can maintain MCP and OpenAPI plugins.
Group Managers
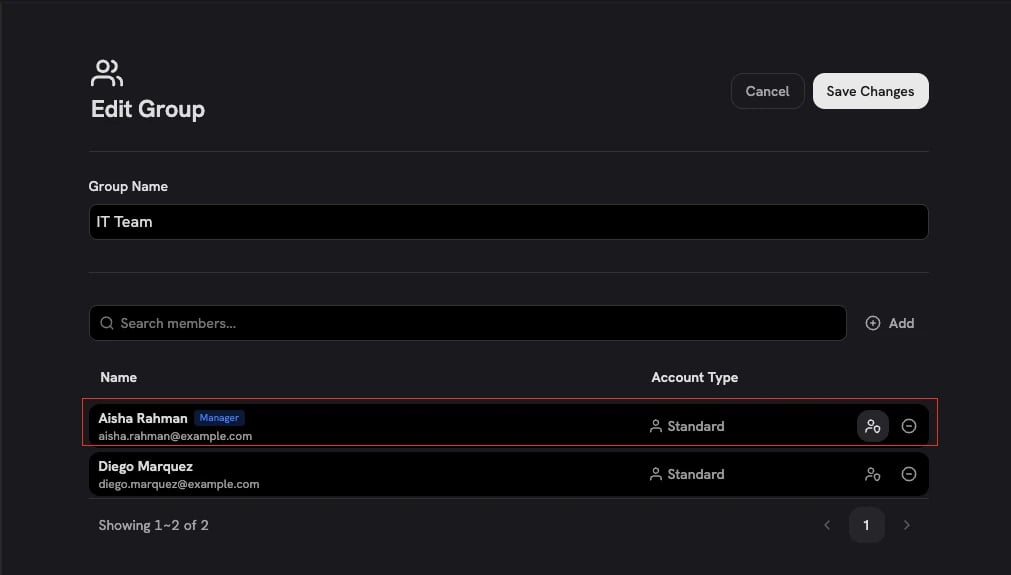
A Group Manager is a user who can manage one specific group from that group’s detail page. Group Managers are useful when a team lead should manage their own team’s users and resources, but should not receive organization-wide admin powers. Scoped to the group they manage, a Group Manager can:- Add and remove members from that group.
- Manage connectors and document sets shared only with that group.
- Manage agents shared only with that group.
- Manage skills shared only with that group.
- Manage plugins through the agents shared with that group.
- Restrict an MCP plugin to the groups they manage. They must select at least one of their groups.
- Manage resources that are not shared with a group they manage.
- Make a resource public.
- Share a resource with a group they do not manage.
- Grant organization-wide permissions.
Group Permission vs. Group Manager
Available Group Permissions
The following permissions can be assigned to custom groups:View Agent Analytics is not scoped through Group Manager access. The permission can be granted to a group,
but agent-level analytics still require the user to own the agent unless the user also has Manage Agents.
Community Edition has no group permission configuration, so Create Agents is available to everyone.
The permissions in this table are configured per group on the Business and Enterprise plans.
Document Access Is Separate
Permissions decide what a user can do in the Admin Panel and which resources they can manage. Document visibility is still controlled by connector and resource access settings. Connectors can be:- Private: Visible only to the creator, plus any groups explicitly granted access.
- Public: Visible to all Onyx users.
- Auto-sync: Restricted using permissions synced from the source system.
- Auto-sync, restricted: Synced permissions apply, and only members of the selected groups can see the documents. Turn on Restrict Access to Groups on the connector. An admin must first turn on Allow Group Restrictions on Permission-Synced Connectors on Security & Hardening. Requires a Business or Enterprise plan.
Common Setups
Frequently Asked Questions
Do service accounts use group permissions?
Do service accounts use group permissions?
Yes. Service accounts receive permissions from their groups exactly like a user. Bot, anonymous,
and external placeholder accounts are system-managed and are not managed like regular users.
How do anonymous users fit into permissions?
How do anonymous users fit into permissions?
Anonymous users only exist when anonymous access is enabled, and they can only reach the chat surface.
They have no account and belong to no group,
so they cannot be given permissions and never appear in the permission layers as a separate level.
Can I create custom roles?
Can I create custom roles?
Yes. Create a custom group and assign the permissions that match the role you want.