Buy New
$89.83$89.83
FREE delivery Monday, October 12
Ships from: Amazon Sold by: Addas LLC
Used - Very Good
$19.98$19.98
FREE delivery October 20 - 23
Ships from: Bahamut Media Sold by: Bahamut Media
Download the free Kindle app and start reading Kindle books instantly on your smartphone, tablet, or computer - no Kindle device required.
Read instantly on your browser with Kindle for Web.
Using your mobile phone camera - scan the code below and download the Kindle app.
Follow the author
OK
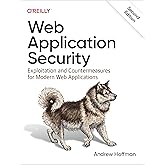
Web Application Security: Exploitation and Countermeasures for Modern Web Applications
Purchase options and add-ons
While many resources for network and IT security are available, detailed knowledge regarding modern web application security has been lacking, until now. This practical guide provides both offensive and defensive security concepts that software engineers can easily learn and apply.
Andrew Hoffman, a senior security engineer at Salesforce, introduces three pillars of web application security: recon, offense, and defense. You'll learn methods for effectively researching and analyzing modern web applications, including those you don't have direct access to. You'll also learn how to break into web applications using the latest hacking techniques. Finally, you'l learn how to develop mitigations for use in your own web applications to protect against hackers.
- Explore common vulnerabilities plaguing today's web applications
- Learn essential hacking techniques attackers use to exploit applications
- Map and document web applications for which you don't have direct access
- Develop and deploy customized exploits that can bypass common defenses
- Develop and deploy mitigations to protect your applications against hackers
- Integrate secure coding best practices into your development lifecycle
- Get practical tips to help you improve the overall security of your web applications
- ISBN-101492053112
- ISBN-13978-1492053118
- Edition1st
- PublisherO'Reilly Media
- Publication dateApril 7, 2020
- LanguageEnglish
- Dimensions7 x 0.75 x 9 inches
- Print length327 pages
There is a newer edition of this item:
$36.31
(20)
Only 9 left in stock (more on the way).
Customers who viewed this item also viewed
- Web Application Security: Exploitation and Countermeasures for Modern Web ApplicationsPaperbackFREE Shipping by AmazonGet it as soon as Monday, Oct 12Only 9 left in stock (more on the way).
Customers also bought or read
- The Web Application Hacker's Handbook: Finding and Exploiting Security Flaws
Paperback$28.01$28.01Delivery Mon, Oct 12 - The Hacker Playbook: Practical Guide To Penetration Testing
Paperback$21.88$21.88Delivery Mon, Oct 12 - Bug Bounty Bootcamp: The Guide to Finding and Reporting Web Vulnerabilities
Paperback$38.10$38.10FREE delivery Oct 27 - Nov 3 - Black Hat Python, 2nd Edition: Python Programming for Hackers and Pentesters
Paperback$35.17$35.17FREE delivery Mon, Oct 12
From the Publisher
From the Preface
Web Application Security walks you through a number of techniques used by talented hackers and bug bounty hunters to break into applications, then teaches you the techniques and processes you can implement in your own software to protect against such hackers.
This book is designed to be read from cover to cover, but can also be used as an on-demand reference for particular types of recon techniques, attacks, and defenses against attacks. Ultimately, this book is written to aid the reader in becoming better at web application security in a way that is practical, hands-on, and follows a logical progression such that no significant prior security experience is required.
Prerequisite Knowledge and Learning Goals
This is a book that will not only aid you in learning how to defend your web application against hackers, but will also walk you through the steps hackers take in order to investigate and break into a web application. Throughout this book we will discuss many techniques that hackers are using today to break into web applications hosted by corporations, governments, and occasionally even hobbyists. Following sufficient investigation into the previously mentioned techniques, we begin a discussion on how to secure web applications against these hackers.
In doing so you will discover brand new ways of thinking about application architecture. You will also learn how to integrate security best practices into an engineering organization. Finally, we will evaluate a number of techniques for defending against the most common and dangerous types of attacks that occur against web applications today.
After completing Web Application Security you will have the required knowledge to perform recon techniques against applications you do not have code-level access to. You will also be able to identify threat vectors and vulnerabilities in web applications, and craft payloads designed to compromise application data, interrupt flow, or interfere with the intended function of a web application. With these skills in hand, and the knowledge gained from the final section on securing web applications, you will be able to identify risky areas of a web application’s codebase and understand how to write code to defend against attacks that would otherwise leave your application and its users at risk.
Suggested Background
The potential audience for this book is quite broad, but the style in which the book is written and how the examples are structured should make it ideal for anyone with an intermediary-level background in software engineering.
Minimum Required Skills
In this book, an “intermediary-level background in software engineering” implies the following:
- You can write basic CRUD (create, read, update, delete) programs in at least one programming language.
- You can write code that runs on a server somewhere (such as backend code).
- You can write at least some code that runs in a browser (frontend code, usually JavaScript).
- You know what HTTP is, and can make, or at least read, GET/POST calls over HTTP in some language or framework.
- You can write, or at least read and understand, applications that make use of both server-side and client-side code, and communicate between the two over HTTP.
- You are familiar with at least one popular database (MySql, MongoDB, etc.).
These skills represent the minimum criteria for successfully following the examples in this book. Any experience you have beyond these bullet points is a plus and will make this book that much easier for you to consume and derive educational value from.
Editorial Reviews
About the Author
Prior to this role, Andrew was a software security engineer working on Locker Service, the world's first JavaScript namespace isolation library that operates from the interpreter level up. In parallel, Andrew also contributed to the upcoming JavaScript language security feature "Realms," which provides language level namespace isolation to JavaScript.
Product details
- Publisher : O'Reilly Media
- Publication date : April 7, 2020
- Edition : 1st
- Language : English
- Print length : 327 pages
- ISBN-10 : 1492053112
- ISBN-13 : 978-1492053118
- Item Weight : 1.15 pounds
- Dimensions : 7 x 0.75 x 9 inches
- Best Sellers Rank: #2,838,959 in Books (See Top 100 in Books)
- #542 in Web Services
- #705 in Web Encryption
- #785 in Computer Cryptography
- Customer Reviews:
About the author

Andrew Hoffman is a Senior Staff Security Engineer at Ripple. He has a unique skill-set which is composed of both software engineering and application security. His primary security interests are client-side attacks, threat modeling and security automation.
He has worked and consulted with a variety of fortune 500 software companies and startups alike, assisting in the development of security programs, threat modeling, secure application architecture and mitigation design for critical risk or high complexity vulnerabilities.
He has also worked with every major browser vendor, including TC39 and the Web Hypertext Application Technology Working Group (WHATWG)—organizations responsible for the upcoming version of JavaScript and the browser DOM spec.
Related products with free delivery on eligible orders
Customer reviews
Customer Reviews, including Product Star Ratings help customers to learn more about the product and decide whether it is the right product for them.
To calculate the overall star rating and percentage breakdown by star, we don’t use a simple average. Instead, our system considers things like how recent a review is and if the reviewer bought the item on Amazon. It also analyzed reviews to verify trustworthiness.
Learn more how customers reviews work on Amazon