Repository navigation
Home
⚠️ This wiki is deprecated. The ModSecurity documentation has moved to https://www.modsecurity.org/docs/ and this wiki is no longer updated.This page now lives at ModSecurity Documentation. Found something outdated or wrong? Edit its source at owasp-modsecurity/documentation; pull requests are welcome.
ModSecurity is an open source, cross platform web application firewall (WAF) engine donated to OWASP in 2024. It has a robust event-based programming language which provides protection from a range of attacks against web applications and allows for HTTP traffic monitoring, logging and real-time analysis. Securing tens of millions of domains, ModSecurity is the most widely deployed WAF engine in existence.
The WIKI has been transferred from Trustwave to OWASP ModSecurity together with the code repo. It is partially outdated and will have to be overhauled. In the meantime, read with caution.
- Frequently Asked Questions TO BE REVIEWED OR ARCHIVED
- Getting Help TO BE REVIEWED OR ARCHIVED
- Reference Manual v2.x (Some people experience difficulty with the rendering for this version of the document)
- Reference Manual v2.x (Split)
- Windows Troubleshooting
- OWASP ModSecurity Roadmap
- OWASP ModSecurity Contributing and development guidance
- Debugging
- Original v3 Motivations & Goals (Blog Post)
These are legacy pages, that are kept around for future reference.
- Overview of Changes TO BE ARCHIVED
- Milestones TO BE ARCHIVED
- Distribution specific packaging TO BE ARCHIVED
- Log Data Format TO BE ARCHIVED
- Tools TO BE ARCHIVED
- Development Roadmap TO BE ARCHIVED
- Ideas Google Summer of Code 2016 TO BE ARCHIVED
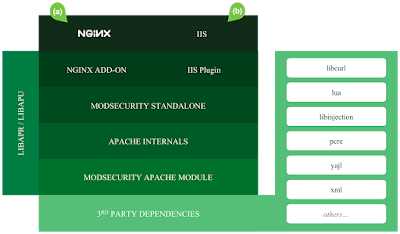
Architecture graphic that is not quite easy to grasp and a caption is missing: